
The Authority in Global Agricultural Chemistry & Bio-Resources
How to Define a Modular System Specification for Interface Control and Expansion
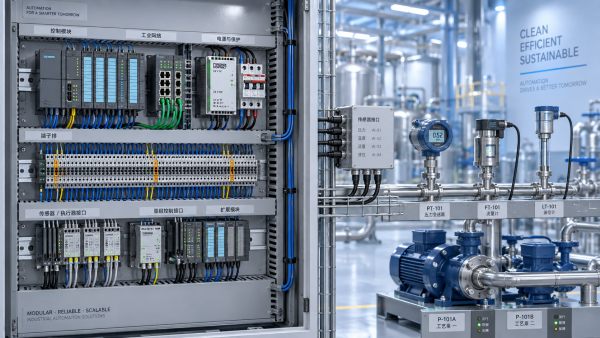
A modular system is only as controllable as its interfaces are defined. A specification that lists modules, nominal capacities, and a preferred communications protocol may look complete, yet still leave critical integration questions unresolved: which component owns a safety interlock, how a replacement module is identified, whether a future expansion can share a power segment, or whether a software update changes a validated operating state.
In regulated and infrastructure-heavy environments, these omissions become lifecycle problems rather than commissioning inconveniences. A skid added to an API process line, a sensor cluster integrated into irrigation automation, or a new pumping unit connected to aquaculture controls must fit not only physically and electrically, but also functionally, procedurally, and within the system’s evidence trail. A sound modular system specification therefore defines the boundaries that must remain stable while allowing the modules inside those boundaries to change.
Start with the system boundary, not the module catalogue
The first question is not which modules are available. It is what the system is responsible for controlling, monitoring, recording, and protecting. The specification should identify the system boundary in operational terms: the process or asset covered, the external systems it depends on, the actions it may command, and the conditions under which it must transfer control or stop safely.
A boundary definition for a grain handling line, for example, may include conveyors, weigh cells, motor control centres, dust extraction status, and local emergency-stop circuits. It may exclude the enterprise resource planning platform while requiring a defined production-data exchange with it. In a chemical process environment, a modular dosing package may own local pump sequencing and pressure protection, while the distributed control system retains plant-level permissives, batch execution, and alarm management. Without this allocation, two systems can both assume responsibility for the same action—or neither can.
Boundary statements should distinguish at least four layers:
- Physical boundary: equipment footprint, mounting points, enclosure interfaces, piping or ducting connection points, service clearances, and environmental limits.
- Energy boundary: incoming electrical supply, protective earth, pneumatic or hydraulic utilities, thermal loads, isolation provisions, and available fault capacity where relevant.
- Control boundary: sensor ownership, actuator authority, operating modes, interlocks, alarms, setpoint sources, and manual override rules.
- Information boundary: data sources, timestamps, protocol responsibilities, historian records, user access paths, retention requirements, and data quality status.
These boundaries should be expressed at the point of connection, rather than as general descriptions of intended operation. “Supports integration with plant controls” is not a usable requirement. “Exposes read-only flow, temperature, module state, alarm state, and diagnostic status through the defined interface, with source timestamps and engineering units” is testable.
Define interface control as a controlled technical baseline
An Interface Control Document (ICD) is the working core of a modular system specification. It should not be treated as a drawing package produced late in the design stage. Its purpose is to establish a controlled agreement between modules and surrounding systems, so that changes are visible and compatibility can be assessed before installation.
Each interface needs a unique identifier and a clear owner. Ownership does not mean commercial ownership; it means accountability for maintaining the interface definition, approving changes, and resolving discrepancies. Where a module supplier provides a local controller but the site owner supplies the supervisory control layer, the ICD must state who controls interface revisions, protocol testing, cybersecurity settings, and fault-response logic.
For physical interfaces, record more than dimensions. Include connector family, pin assignment, mating requirements, cable type and length constraints, ingress protection conditions, grounding arrangement, torque or sealing requirements, and permitted field modifications. A mechanically compatible connection can still fail if vibration, washdown exposure, chemical compatibility, electromagnetic environment, or maintenance access has not been considered.
Electrical interfaces require rated and maximum values, not only nominal values. Specify supply voltage tolerance, frequency, inrush current, steady-state load, peak demand, protective device coordination, isolation requirements, earthing scheme, power-quality constraints, and behaviour following supply loss and restoration. Expansion plans often fail because spare capacity was calculated from nominal consumption while overlooking startup loads, heater duty cycles, or the derating imposed by enclosure temperature.
For control and data interfaces, the specification should define:
- the protocol and applicable profile or version;
- network topology, addressing convention, media, and redundancy expectations;
- message structure, data types, engineering units, scaling, and valid ranges;
- update rates, latency limits, timeout behaviour, and communication-loss response;
- time synchronization source and timestamp treatment;
- command acknowledgement, sequence handling, and state-transition rules;
- alarm priorities, latching behaviour, reset authority, and event logging;
- authentication, authorization, certificate handling, and remote-access restrictions where connected systems are involved.
A protocol name alone does not establish interoperability. Two devices may both support Modbus TCP, OPC UA, EtherNet/IP, or another industrial protocol while differing in object models, register mapping, alarm semantics, security settings, or connection limits. The specification must identify the exact implemented interface, not merely the family of technologies permitted.
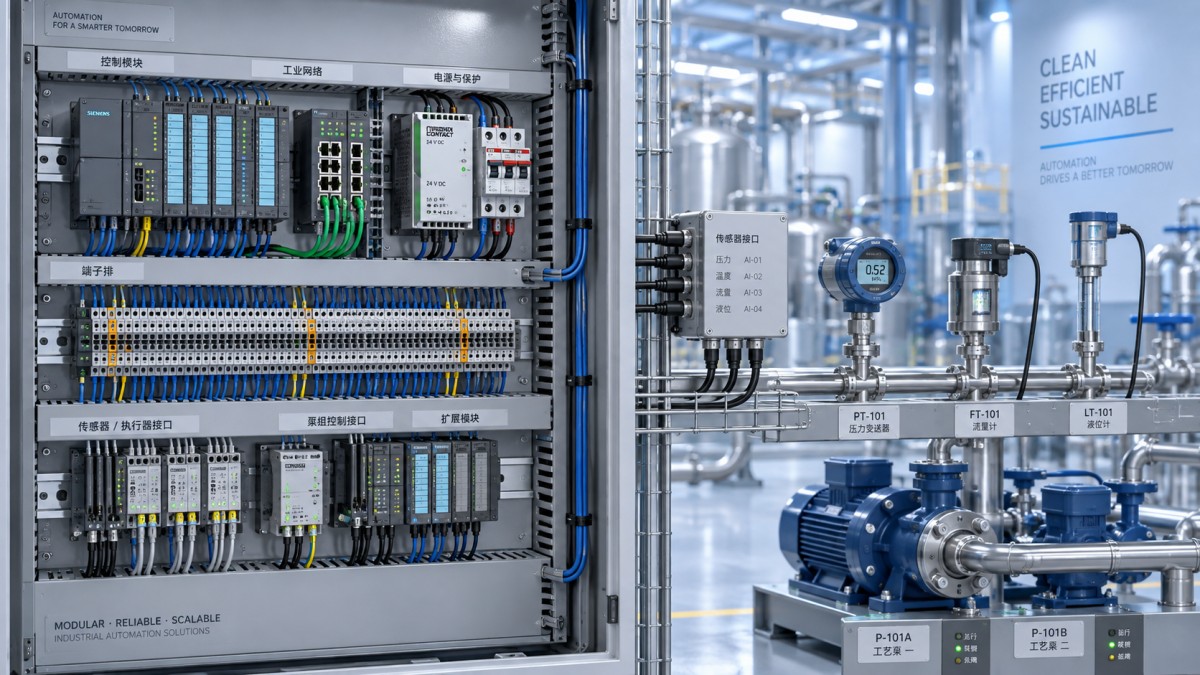
Make functional behaviour explicit at module boundaries
Modularity is frequently confused with independence. In reality, a module can be mechanically self-contained while remaining tightly coupled to upstream quality conditions, downstream capacity, shared safety functions, or common utility availability. Functional dependencies need to be specified in terms of states and transitions.
A useful model defines normal operating states, startup, shutdown, cleaning or maintenance states where applicable, fault states, and recovery states. For each state, identify the inputs required to enter it, the outputs produced, the controls that are enabled, and the response to missing or invalid external signals. This is particularly important where a module can operate locally but is normally coordinated by a wider automation platform.
Consider a modular filtration or extraction unit. The unit may report “ready,” but that status has limited value unless the conditions behind it are defined. Does “ready” mean power is available, local faults are absent, cleaning is complete, valves are in their starting positions, upstream material is available, and downstream receiving capacity has been confirmed? A specification should avoid composite status signals whose meaning depends on undocumented logic.
Safety-related functions require separate treatment from routine process control. The required performance, architecture, proof-test arrangements, and independence of safety functions must be determined under the standards and regulatory regime applicable to the installation. A modular specification should identify safety interfaces, cause-and-effect requirements, reset conditions, bypass controls, and diagnostic coverage expectations, but should not assume that a supplier’s internal protective function can automatically satisfy the overall site safety function.
The same discipline applies to quality-critical functions. In pharmaceutical or food-related processes, a module may generate measurements or records that support release, traceability, or process verification. The specification must identify whether those records are informational, operational, or quality-critical; whether they are editable; how changes are audited; and how the record remains attributable to the relevant batch, lot, or operating interval.
Specify expansion as capacity plus compatibility
“Expandable” has little technical value unless it is converted into measurable constraints. Expansion is not simply the ability to attach more modules. It is the ability to add defined capacity without violating performance limits, safety assumptions, network rules, documentation controls, or validation status.
The specification should state the intended expansion envelope. This may include the maximum number of module positions, permitted aggregate load, reserved panel space, spare I/O, network node limits, address capacity, cooling allowance, structural loads, hydraulic headroom, and software licence dependencies. Each reserve should be tied to an assumption. Spare ports are not useful if the controller lacks processing margin, the network switch lacks power budget, or the cabinet heat dissipation limit has already been reached.
Expansion also changes system dynamics. Adding pumps may alter pressure transients. Adding sensors can increase scan times or network traffic. Adding a tank can change residence time and cleaning coverage. Adding a motor-driven agricultural implement can affect voltage drop and protection coordination. The baseline specification should therefore identify parameters that must be reassessed when a module is added, including process capacity, control-loop tuning, network performance, power quality, utility demand, emergency-stop zoning, and environmental loading.
Where modules may be supplied over a long lifecycle, version compatibility needs its own rules. Define whether a new module must remain backward compatible, whether adapters are allowed, which firmware combinations are approved, and how deprecated interfaces are handled. A modular architecture becomes fragile when revision control exists only in supplier documentation rather than in the site’s controlled configuration record.
Use a compatibility matrix rather than relying on narrative claims
Compatibility statements are strongest when presented as a matrix linking module types to interface requirements, operating conditions, and verification evidence. This prevents a common failure mode: approval of a module based on one compatible feature while its other dependencies remain unexamined.
The matrix should distinguish “compatible as supplied,” “compatible with defined adaptation,” and “not permitted.” Treating all compatibility as binary conceals the cost and risk of adapters, custom code, or site-specific settings. An adapter may be acceptable for a non-critical monitoring signal and unacceptable for a safety command or regulated electronic record.
Documentation is part of the interface, not an administrative attachment
A module that cannot be identified, configured, tested, maintained, and replaced from controlled records is not fully modular in operational terms. Documentation requirements should be embedded in the modular system specification from the beginning.
The minimum controlled set commonly includes interface drawings, wiring and network diagrams, tag lists, I/O lists, communication maps, functional descriptions, alarm and interlock schedules, software and firmware versions, configuration backups, calibration requirements, maintenance instructions, spare-parts definitions, and test protocols. The precise set depends on the application, but the governing principle is stable: every defined interface must have evidence that it was built and verified as specified.
In environments subject to GMP expectations or formal environmental obligations, documentation also needs to support change assessment. A replacement sensor with the same measured range may still differ in wetted materials, calibration method, firmware, diagnostic behaviour, or electronic record handling. The specification should require a change classification process that decides whether the replacement is like-for-like, requires partial retesting, or affects validated status.
Acceptance criteria should test integration, not just individual modules
Factory tests can confirm that a module operates in isolation. They do not prove that it behaves correctly when connected to real utilities, field devices, supervisory software, and abnormal operating conditions. Acceptance criteria should include interface-focused tests: loss of communications, power restoration, invalid sensor values, conflicting commands, alarm acknowledgment, module removal where permitted, configuration restoration, and expansion-node discovery.
Traceability matters here. Each requirement should map to a verification method—inspection, analysis, demonstration, or test—and to an acceptance record. Vague wording such as “system shall be user-friendly” or “equipment shall support future integration” cannot be verified consistently. Requirements should define observable conditions, limits, and pass criteria.
The strongest modular system specification is therefore not the longest one. It is the one that makes interface responsibilities, allowable variations, evidence requirements, and expansion limits unambiguous. When those elements are controlled, modules can change without turning every change into a redesign of the whole system. When they are not, apparent flexibility merely shifts uncertainty from initial design into commissioning, compliance review, and long-term maintenance.
Related Intelligence
- APIs & IntermediatesHow to Define a Modular System Specification for Interface Control and ExpansionModular system specification guide: define interface control, safety ownership, data rules, and scalable expansion for reliable integration and lifecycle confidence.
- APIs & IntermediatesQuotation Planning for Strategic Sourcing: How Buyers Compare Supplier BidsQuotation planning sourcing helps buyers compare supplier bids beyond price. Learn to assess scope, compliance, lead times, risk, and total cost for smarter sourcing decisions.
- APIs & IntermediatesHow to Qualify a Purified Bioprocess Materials Supplier for GMP ManufacturingPurified bioprocess materials supplier qualification guide for GMP manufacturing: assess traceability, contamination control, change notification, and supply reliability.
The Morning Broadsheet
Daily chemical briefings, market shifts, and peer-reviewed summaries delivered to your terminal.